“JobHunger handles sensitive resumes and employment data every day. Cynarks ran a thorough penetration test across our candidate portal, parsing pipelines, and auth flows — then re-tested the fixes. We shipped with confidence.”
Cynarks delivers penetration testing, red team, 24/7 SOC, and cloud security reviews. Every finding is engineer-validated. Critical and high issues include a free retest after you remediate.
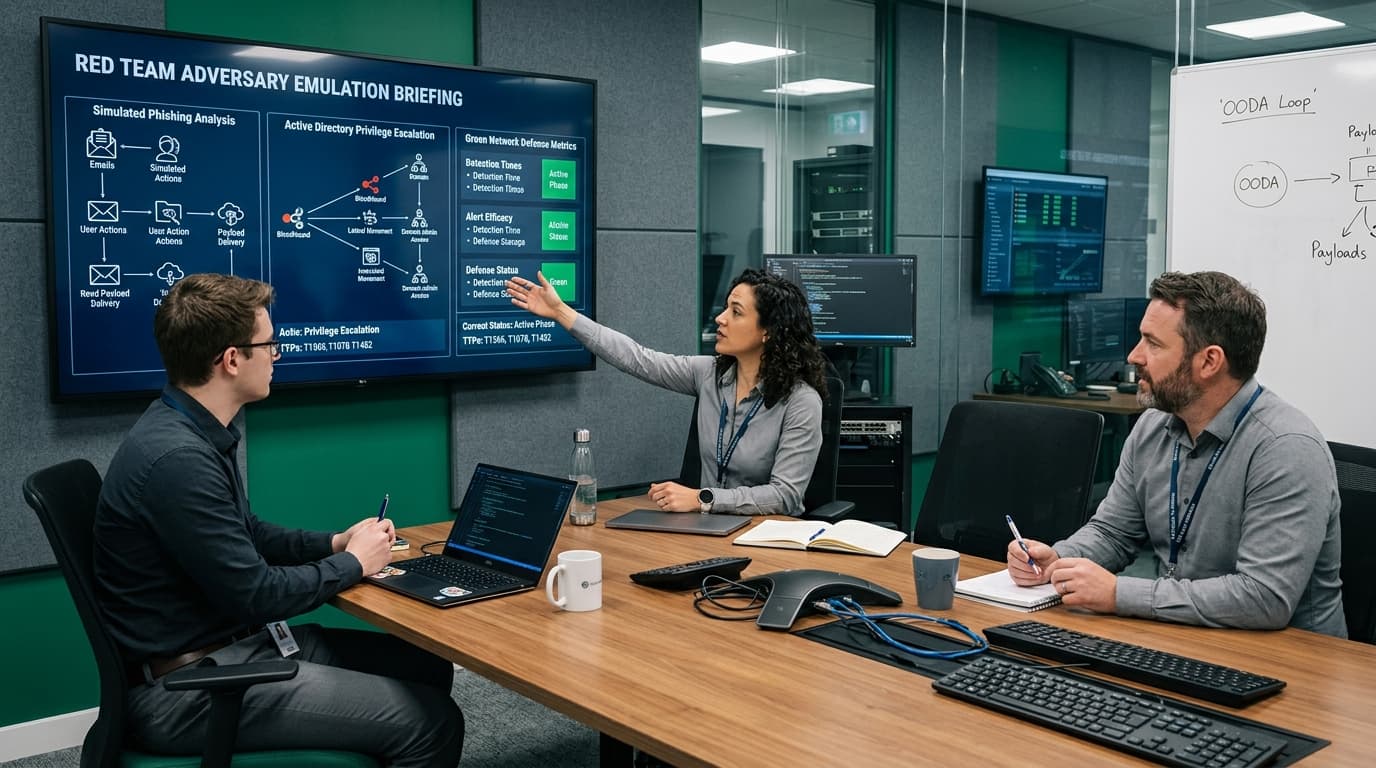
From manual VAPT and red team to 24/7 managed SOC, cloud reviews, AppSec, compliance readiness, training, and vCISO — scoped and delivered by the same practitioners.
How we work — not vanity metrics
Madhapur-based practitioners define in-scope assets, hand-validate every finding, deliver PoCs and remediations, then retest critical and high issues at no extra charge.
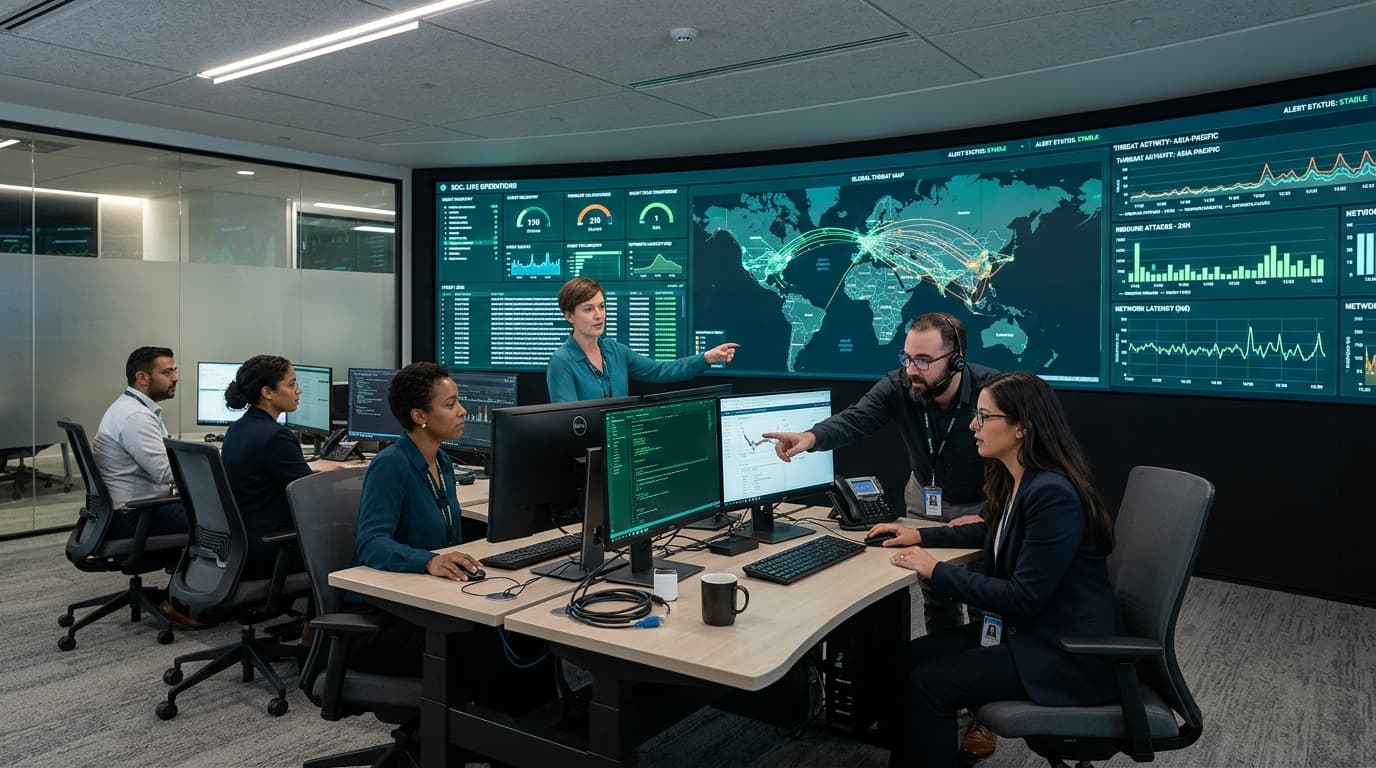
Hyderabad analysts triage SIEM, EDR, and cloud alerts on shift — with a written escalation matrix for confirmed incidents, not dashboard noise.
OSCP, CEH, CISSP, and CISA engineers run scoping through report delivery themselves — no offshore subcontractor handoff mid-engagement.
Every finding is hand-validated, CVSS-scored, and tied to exploitability so developers fix confirmed risk instead of chasing scanner false positives.
After you remediate, we retest critical and high findings at no extra charge. The engagement closes when those risks are verified fixed.
Fintech, healthcare, SaaS, education, and manufacturing get threat models and control maps matched to their regulators and blast radius.
Executive summary for leadership, engineering report with reproduction steps, remediation priority, and an attestation letter for customers or auditors.
BFSI, healthcare, SaaS, manufacturing, and more — each card lists a typical engagement window, standards we map to, and the attack paths we prioritize first so procurement knows exactly what the work covers.
Same four phases on every penetration test and offensive assessment: scope the attack surface, validate findings by hand, deliver CVSS-scored reports, then retest critical and high fixes.
Confirm rules of engagement, map architecture and stack, then enumerate public and internal attack surface so VAPT stays on authorized, reachable targets only.
Automated tooling plus manual testing across web, API, mobile, and network. Every finding is validated by hand; controlled exploitation shows what an attacker could actually achieve.
Findings get CVSS scores and business context, then land as two clear packs: an executive summary for leadership and an engineering report with evidence and reproduction steps.
Work continues after delivery. We help prioritize fixes, retest critical and high findings, and leave you with a practical cadence for the next assessment cycle.
Quotes from JobHunger, Syncpedia, and Skavyra — Hyderabad platforms that engaged Cynarks for production web and API penetration testing.
Headquartered in Madhapur, Ayyappa Society, near HITEC City. Penetration testing, red team, 24/7 managed SOC, cloud security reviews, ISO 27001 / SOC 2 readiness, vCISO advisory, and practitioner-led training.
Cynarks is a cybersecurity firm in Madhapur, Hyderabad. We deliver penetration testing (VAPT), red team operations, 24/7 managed SOC, application and cloud security (AWS / Azure / GCP), ISO 27001 / SOC 2 / PCI DSS readiness, vCISO advisory, and practitioner-led training.
Browse servicesOSCP, CEH, CISSP, and CISA practitioners lead engagements. Findings are manually validated, CVSS-scored, and backed with reproduction steps. Critical and high issues get a free retest after remediation. Preview sanitized sample reports on the Reports page.
View sample reportsHeadquarters: Madhapur, Ayyappa Society, Hyderabad (near HITEC City). We support clients across India and abroad for offensive testing, 24/7 managed detection, cloud reviews, and compliance advisory.
Contact usEight online, practitioner-led tracks: Cyber Security & Ethical Hacking, SOC Analyst (Blue Team), Advanced Penetration Testing, Web Application Security, Bug Bounty & Bug Hunting, Digital Forensics & Incident Response, Cloud Security (AWS & Azure), CompTIA Security+ Essentials. Each includes cyber-range labs, attack simulations, and mentor-reviewed portfolio projects.
See all programsYes. Live technical webinar every Friday at 8:00 PM IST — attack-and-defense demos on safe lab targets, live bug hunting, and career Q&A.
Register on WhatsAppCall or WhatsApp +91 73373 81478, email security@cynarks.com, or use the contact form. An engineer reviews every enquiry. Assessments start with a free scoping call; training enquiries get a counselling call with syllabus details.
Get in touchSector plans for BFSI & fintech, healthcare, government, e-commerce, telecom, manufacturing, education, energy, and SaaS — each with typical engagement windows, standards we align to, and the risks we test first.
IndustriesTalk to a Cynarks engineer in Hyderabad. We map in-scope apps and networks, propose a realistic test window, and outline deliverables — so you know exactly what the engagement covers before you commit.
Madhapur · +91 73373 81478 · security@cynarks.com